 Many businesses do not fully understand the critical importance of having a strong security architecture until it is too late. However, implementing security architecture can be a confusing process for many growing enterprises. Security architecture consists of various preventive, detective, and corrective controls that businesses choose to implement to protect their applications and infrastructure.
As technology continues to evolve, businesses must keep pace to ensure that their systems remain protected from intruders. Building a strong security architecture can protect a business from countless external threats. It can also help organizations swiftly identify and eliminate threats.
Importance of Security Architecture for Businesses
Having a strong security architecture is no longer just a recommendation for businesses but a necessity. As hackers become more adept at discovering security gaps, it is up to businesses to find new strategies for blocking their attempts. A resilient security architecture framework can be used to protect a company’s most sensitive informational assets. There are countless benefits that come from implementing a strong security architecture, including fewer breaches of your system’s architecture.
Maintaining your security architecture can also be useful for other reasons, such as compliance with key data security standards. There is a good chance that your business is subject to various information security standards, such as HIPAA, PCI DSS, GLBA or GDPR. These data security standards often require a business to maintain an architecture that is well-monitored with certain safety measures implemented. It is also important to remember that these standards are updated frequently, so businesses must continually make changes to address ever-evolving threats.
Most importantly, a strong security architecture can help prevent the loss of business. All it takes is one cyber security breach for your customers to lose trust in your business. A data breach could result in a massive drop in sales, which could force you to shut your doors for good.
Building a Strong Foundation
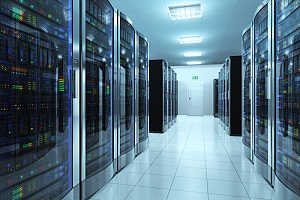 It is not always clear where businesses should begin when building a foundation for their security architecture. However, many experts suggest making data centers a main priority. While many organizations choose to protect users’ systems first, hackers are often more inclined to go directly to data centers. When implementing data center security, establish security zones between workloads and applications, and conduct routine penetrating testing of the segmentation to ensure that your controls remain effective.
It is also important to take user base architecture into consideration. Today, most users are mobile and many do not even visit corporate offices. This means that these professionals should utilize VPNs to maintain a secure connection when conducting work, but most fail to work on a secured server. This leaves these professionals open to certain digital risks. To reduce these risks, standardization should be applied to create a secure user environment. Cloud-computing has also become a go-to for modern businesses that want to leverage services like email conveniently on the cloud. Best of all, mobile users can connect from nearly anywhere.
Raising Awareness of Cyber Security Threats
Cyber security threats are becoming more commonplace in today’s society and although modern businesses are becoming more equipped to deal with these threats, they cannot yet be eliminated. With emerging technologies like the Internet of Things (IoT), along with the rapid growth of the web, organizations must make extra efforts to protect their companies from risks that threaten their livelihood. Security architecture takes on many forms and can lead to a stronger reinforcement against cyber security threats.
Today, cyber security threats are not just limited to email phishing. These threats have become more complex and more difficult to identify. Some of the most common attacks include social engineering, whaling, and phishing, as well as attacks via malware and ransomware. Lately, there has been an uptick in attacks on the Internet of Things. This includes smart homes, cars, and other infrastructure that all make up the IoT. This emerging technology still has many vulnerabilities that hackers exploit to gain access to a wealth of valuable information. Smartphones have also become a common gateway for criminals with the increase of disreputable applications and plugins now available for both Android and Apple devices.
Speak to an Experienced Cyber Security Expert Today
 In a digital world, safeguarding the security of sensitive data is critical for businesses in all industries. Unfortunately, many businesses struggle with the preservation of confidentiality of information used in business applications, processes, and technology. When was the last time that you assessed how secure your enterprise architecture is? If it has been many months or even years, consider investing in cyber security solutions.
Vaultes Enterprise Solutions offers a variety of cyber security solutions designed to protect the integrity of your IT infrastructure. For more information about the foundation of a strong security architecture, request a consultation with a cyber security expert at Vaultes Enterprise Solutions.
 Pen tests are also occasionally known as white hat attacks because it involves a benevolent party’s attempt to break into a system. Companies should perform penetration tests regularly — at least once a year — to ensure their Information Technology (IT) infrastructure remains strong and well-protected. Although tech companies and financial services organizations most frequently perform penetration testing, all types of organizations can greatly benefit from conducting this type of evaluation.
 When an organization performs penetration testing depends on multiple factors, including:
 Pen tests also offer insight into which channels in your organization or application are most at risk and thus what types of new security tools you should invest in or protocols you should follow. This process could help uncover several major system weaknesses you may not have even thought about.
 Speak to the experienced cybersecurity analysts at Vaultes Enterprise Solutions in Reston, Virginia, to learn more about the benefits of penetration testing and/or to schedule such a service. Vaultes is a Veteran Owned Small Business (VOSB) that provides top cybersecurity and risk management solutions to both commercial and federal clients, thanks to highly technical expertise and specialized training. Vaultes’ pen testing division utilizes strategic hacker maneuvers in a controlled environment in order to uncover any potential vulnerabilities before they can be taken advantage of. Vaultes will also guide you on compliance issues.
 Every organization in today’s increasingly dangerous world should make it a priority to address its IT infrastructure’s vulnerabilities and how to protect it from
 Ideally, organizations should perform penetration testing at least once a year. This process should especially be conducted whenever an organization:
 This reconnaissance step involves the collection of preliminary data about a target so that a cyberattack can be more adequately planned. This step also includes establishing the test’s scope and deciding which evaluation processes to use. The five most common types of penetration testing methods are external testing, internal testing, blind testing, double-blind testing and targeted testing. External penetration tests focus on the assets of an organization that are visible online. In internal pen testing, meanwhile, a tester who has access to an application behind its firewalls simulates a cyberattack from a malicious person on the inside. In blind testing, a tester only knows the name of the target, and in double-blind testing, both the tester and the target are in the dark about the cyberattack. Finally, targeted testing involves security personnel and the tester collaborating and keeping each other informed of their respective actions.
 Perhaps the most important step in performing penetration testing involves the compiling of results in a detailed report that links each vulnerability to its corresponding threat. This can help company executives devise more specific solutions to its system’s weaknesses and build stronger defenses (like web application firewalls) against potential threats in the future to make sure no sensitive data is compromised ever again. Such an analysis should also note the amount of time the penetration tester was able to stay in the system undetected.
 All organizations face a certain level of IT threats, especially in this day and age where most business processes have been digitalized. To minimize and eliminate certain risks, modern companies turn to cyber security practices. What is cyber security, exactly?
 Cyber attacks can present themselves in a wide variety of ways. Oftentimes, businesses do not even know that their system or network has been infiltrated until it is too late. Phishing attacks are one of the most common forms of social engineering which can affect any business that uses email. APTs can result in the theft of high-value data, such as information in sectors like manufacturing, national defense, and the finance industry. Malware can also come in several forms, such as keyloggers, viruses, spyware, and worms.